Prisma SASE: work without limits, defend without doubt
Best-in-class security, an exceptional user experience and streamlined operations on one platform with AI-powered Prisma SASE.
Work is hybrid. Threats are smarter. Your data is everywhere.
Employees connect from the office, home and the road, and the network has to keep pace without missing a beat. Attackers using AI exploit the opportunities hybrid work creates, and data knows no boundaries. Delivering consistent policy and a good user experience with separate VPN, proxy and SD-WAN products is increasingly hard.
Prisma SASE converges networking and security on one cloud-delivered platform: it lets people work securely on any device, protects sensitive data against every risk, accelerates application performance and proactively prevents performance issues. Palo Alto Networks was named a Leader in the 2026 Gartner® Magic Quadrant™ for SASE Platforms.
Four promises of Prisma SASE
Work securely anywhere
Empower your team to work securely without limitations on any device.
Data protection
Lock down leaks and protect sensitive data across all channels with unified policies.
Application performance
Fix performance issues before users notice, with acceleration and proactive digital experience monitoring.
AI-powered security
Protect every user, device and location with adaptive, AI-powered security.
Prisma SASE components
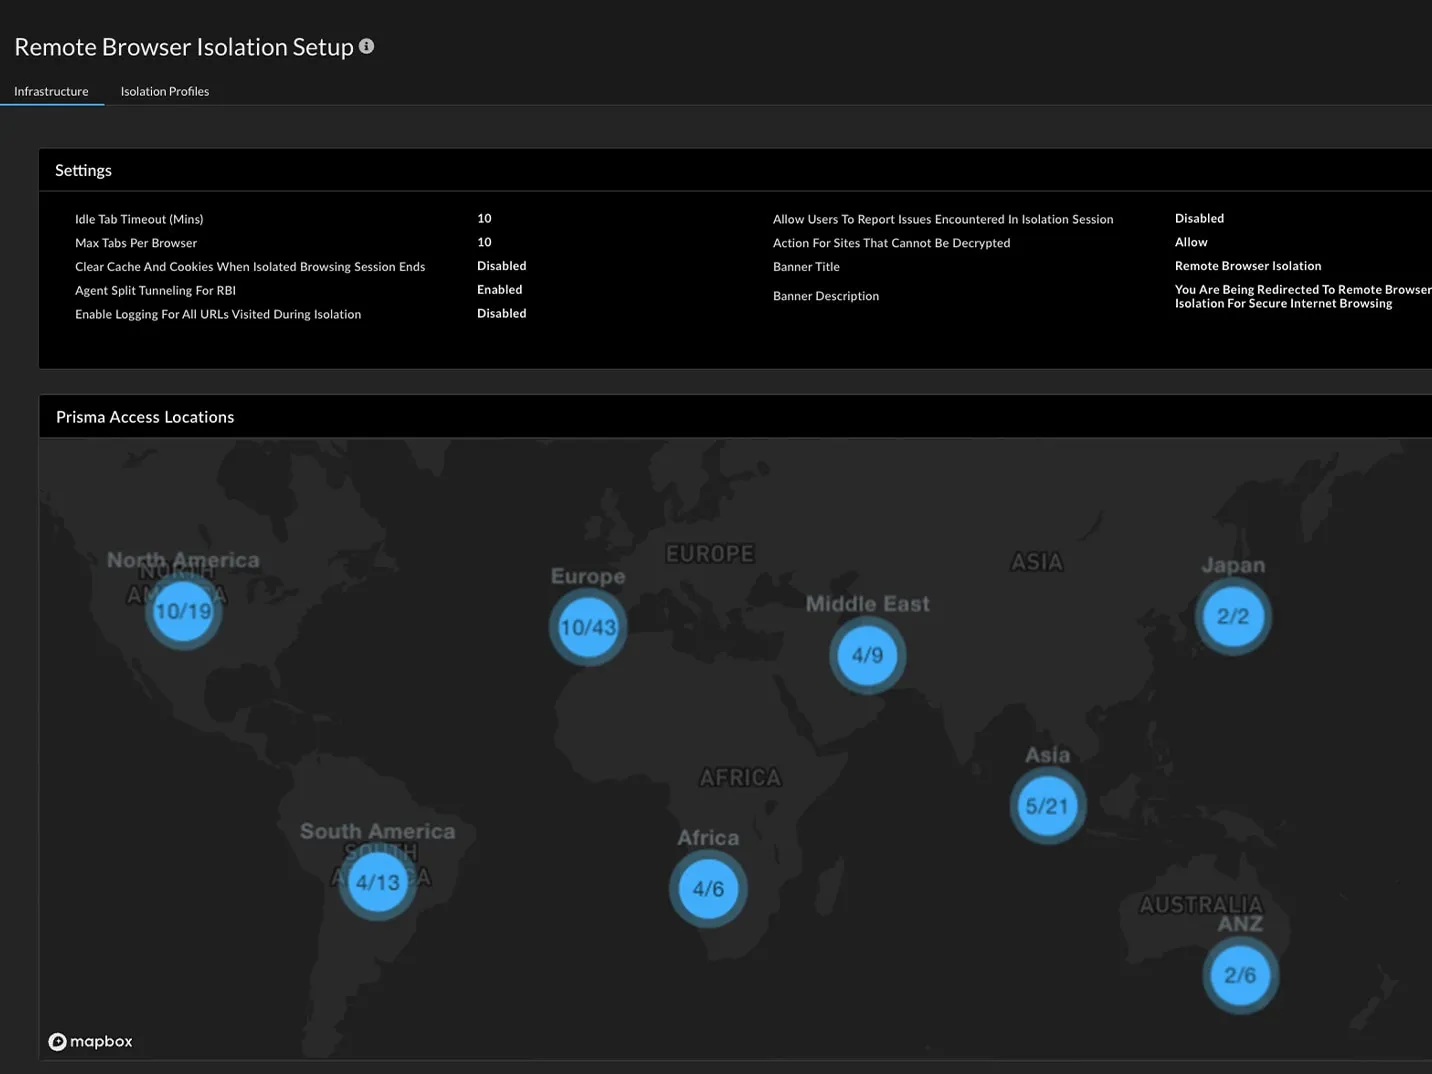
- Prisma Access: cloud-delivered security service edge (SSE): ZTNA 2.0, SWG, CASB, FWaaS and remote browser isolation.
- Prisma Browser: a secure enterprise browser for managed and unmanaged devices.
- Prisma SD-WAN: application-aware SD-WAN for branches with integrated Zero Trust.
- ADEM: end-to-end digital experience monitoring from user to app, with automated troubleshooting.
- AI Access Security and Enterprise DLP: safe use of generative AI apps and enterprise data loss prevention.
Prisma SASE with Albisec
We manage the move from VPN to SASE in measurable phases, with users and business continuity at the centre.
- Analysis of your current VPN, proxy, branch and WAN architecture
- A phased migration plan per user group and location
- Design and rollout of ZTNA, SWG, CASB and DLP policies
- 24/7 support after go-live with digital experience monitoring (ADEM)
Official product page:paloaltonetworks.com/sase
Prisma SASE products
Frequently asked questions
What is SASE?
Secure Access Service Edge is an architecture that combines SD-WAN with security services such as ZTNA, SWG, CASB and FWaaS in one cloud-delivered service, so the same policy and protection apply wherever the user is.
What is the difference between SASE and SSE?
SSE (Security Service Edge) covers the security components of SASE (ZTNA, SWG, CASB, FWaaS). SASE adds the networking side, SD-WAN. Prisma Access SSE together with Prisma SD-WAN forms Prisma SASE.
How do we migrate from our current VPN to SASE?
Typically remote users move to Prisma Access first, then branches connect through Prisma SD-WAN or existing NGFWs. We plan the migration in phases by user group.
Talk to our experts about your Palo Alto Networks project
A new deployment, a firewall migration or a support contract: tell us what you need and we will map out the right path with a free initial assessment.