AI Supply Chain Security: trust what is inside your AI
Deploy AI models and agent skills with confidence. Scan them for threats before they reach production and block unsafe artifacts with policy.
AI models and skills hide risks you cannot see
Open-source models, agent skills, plugins, MCP servers and dependencies speed up development, but an unscanned component can expose data and credentials. AppSec tools cover code, not AI artifacts, and policy checks before production are often missing.
Prisma AIRS AI Supply Chain Security (formerly AI Model Security) scans third-party and internal models and agent skills end to end, including code, prompts, dependencies and MCP usage. According to Palo Alto Networks, more than 3 million third-party artifacts have already been pre-scanned.
AI artifact scanning designed for enterprise speed
Unified coverage
Assess models, skills, prompts, dependencies and MCP usage in one scanning process.
Catch threats before deployment
Detect what traditional tools miss: model backdoors, malicious skill instructions and exfiltration paths.
Block unsafe artifacts
Stop unlicensed, unverified or unapproved models and skills with policies across development and production.
Scan locally or in the cloud
Keep sensitive artifacts in your environment, or check against pre-scanned third-party artifacts in the cloud.
Continuous monitoring
Get automated alerts on new threat findings, including for previously approved artifacts.
Fits existing workflows
Integrate with CI/CD and model registries without slowing developers down.
AI Supply Chain Security with Albisec
As a Palo Alto Networks partner, we run AI security projects end to end, from discovery to production.
- An initial assessment that inventories your AI applications, agents and models
- Selection and licensing of the Prisma AIRS components that fit your use cases
- Deployment, policy design and integration with your existing NGFW, Prisma Access and Cortex environment
- 24/7 support, periodic policy reviews and reporting after go-live
Official product page:paloaltonetworks.com/ai-security/ai-supply-chain-security
More in the AI security family
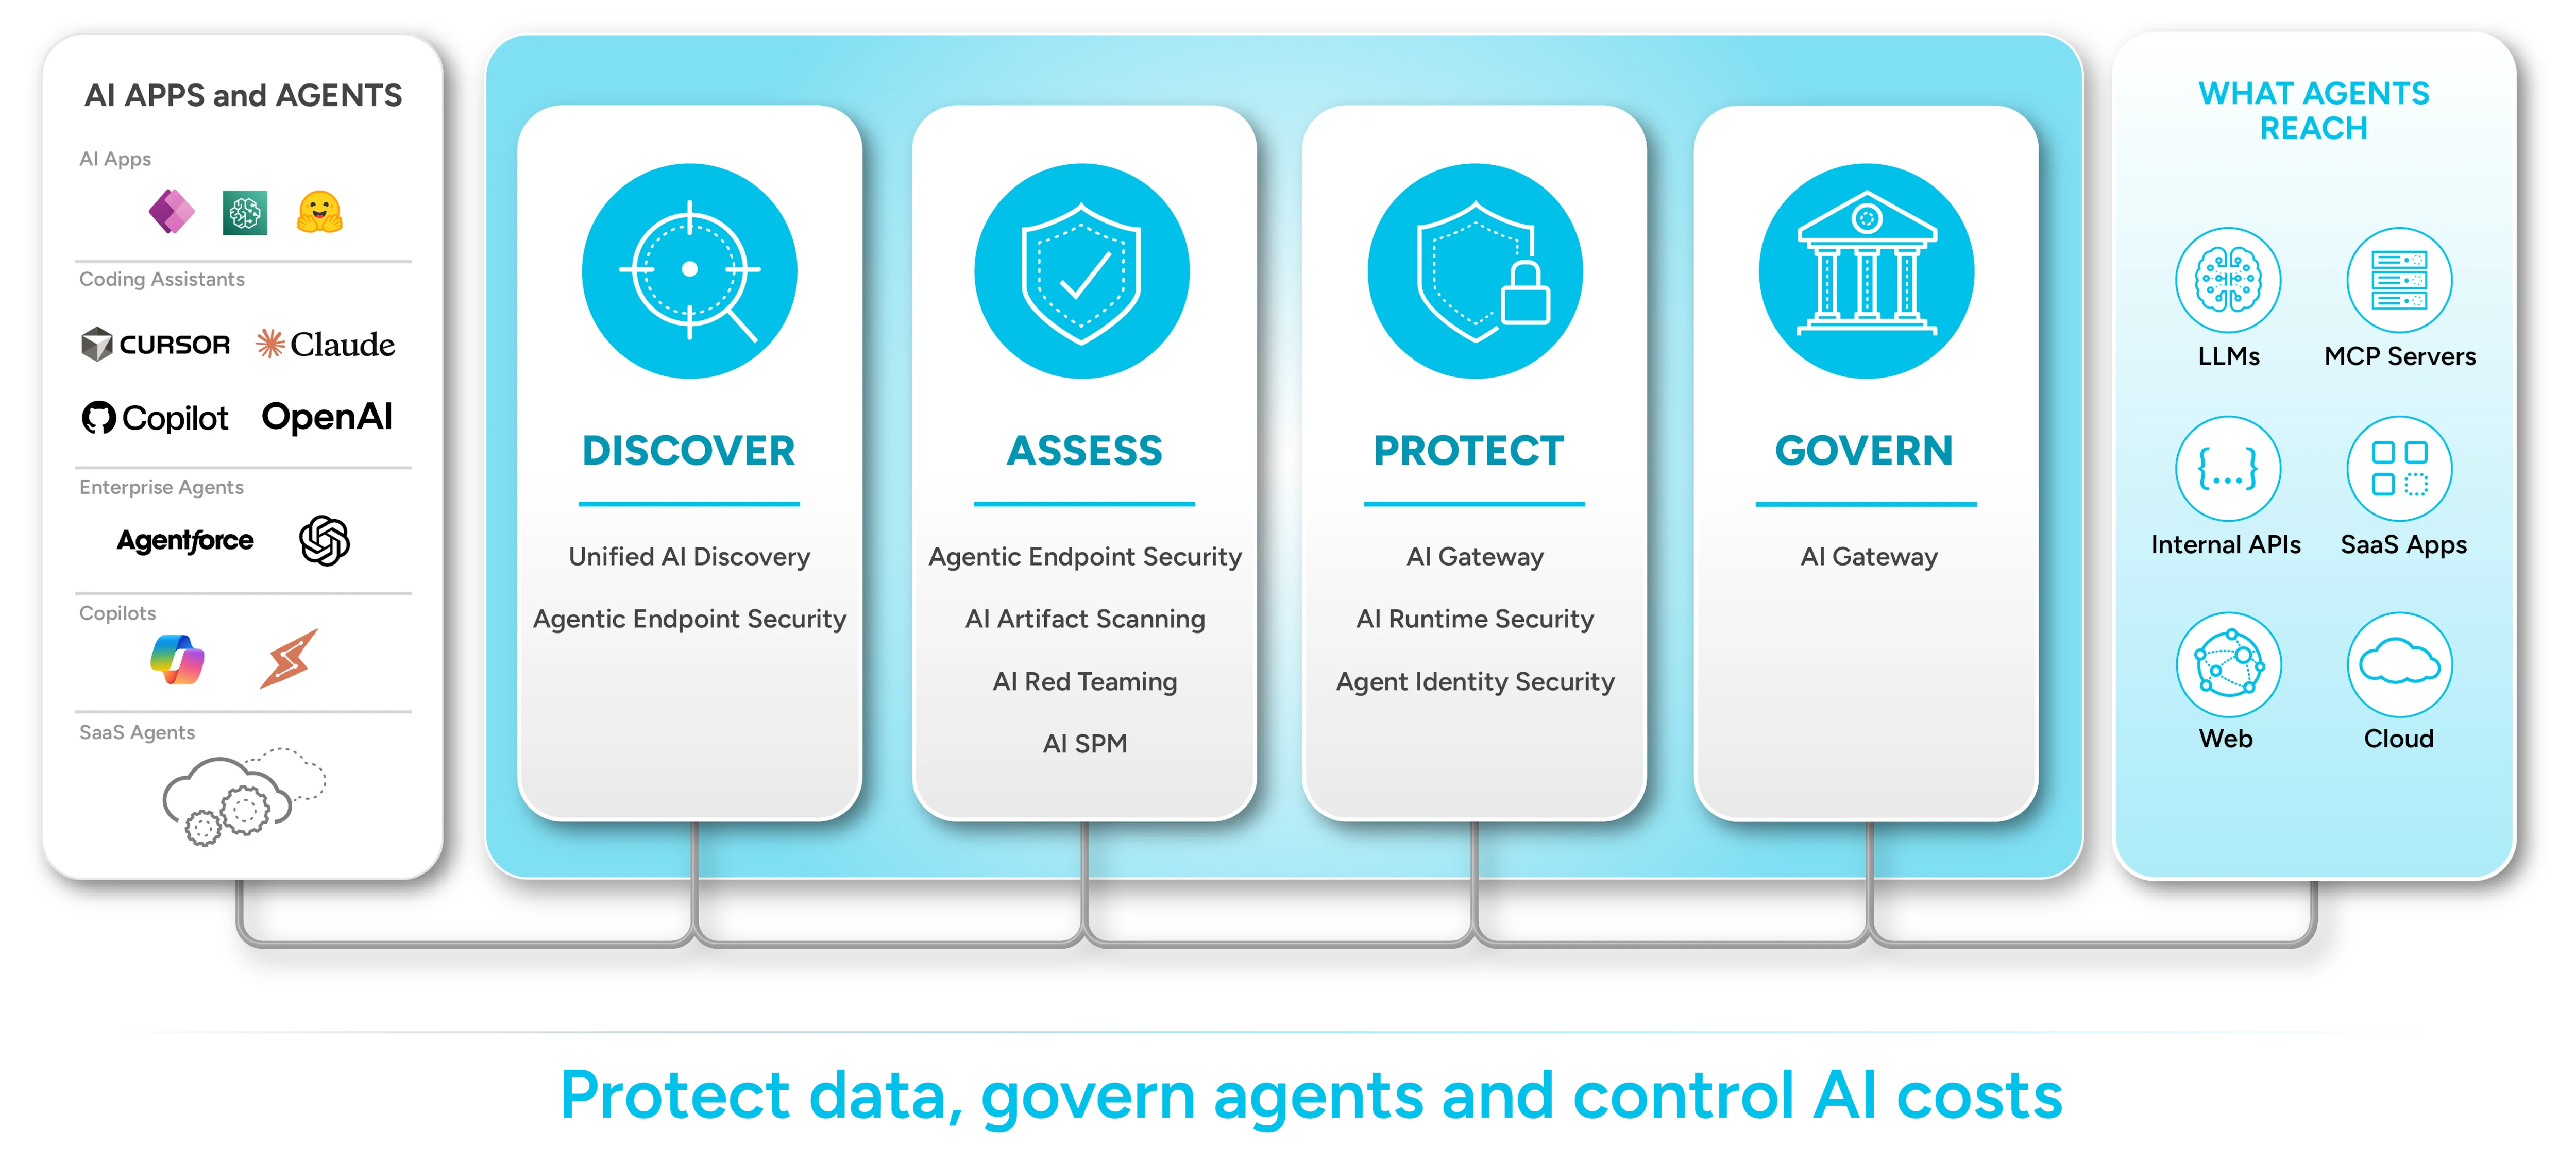
Prisma AIRS
End-to-end security platform for AI apps, agents, models and data.
Learn morePrisma AIRS AI Gateway
Central policy, observability and cost control for LLM, MCP and agent traffic.
Learn morePrisma AIRS AI Runtime Security
Inspects live AI traffic to stop prompt injection and data leakage.
Learn morePrisma AIRS AI Red Teaming
Continuously tests agents and apps with realistic, context-specific attacks.
Learn moreAI Security Posture Management
Visibility and risk prioritisation for models, datasets and agents in the cloud.
Learn moreAgent Identity Security
Agent registry, cryptographic identity and authorisation controls.
Learn moreCortex Agentic Endpoint Security
Visibility and real-time prevention for agents, MCP servers and extensions on endpoints.
Learn moreFrequently asked questions
Why does AI supply chain security matter?
Ready-made models and agent skills can carry threats such as deserialization attacks, model tampering or hidden instructions. Once in production they gain access to internal data and systems, so they must be scanned before deployment.
Which artifacts can be scanned?
Third-party and internal models, agent skills, prompts, dependencies and MCP usage.
Do our models have to be sent to the cloud?
No. Sensitive artifacts can be scanned locally; the cloud is only used to check against pre-scanned third-party artifacts.
Talk to our experts about your Palo Alto Networks project
A new deployment, a firewall migration or a support contract: tell us what you need and we will map out the right path with a free initial assessment.