Palo Alto Networks Advanced Threat Prevention
Stop zero-day threats and intrusions in real time. Protect your network against unknown threats with a next-generation IPS powered by AI and deep learning.
Advanced threat prevention: protect your network against unknown threats
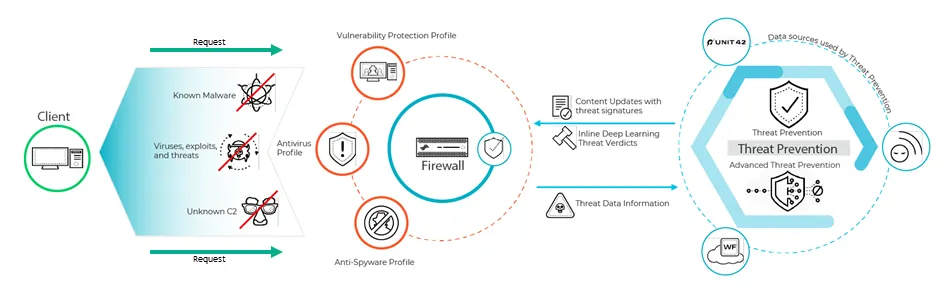
In today’s complex threat landscape, traditional security tools struggle to keep up with increasingly sophisticated attacks. Palo Alto Networks offers Advanced Threat Prevention (ATP), a next-generation IPS designed to stop advanced threats. ATP combines signature-based detection with AI and machine learning to protect every entry and exit point of your network.
Key capabilities: multi-layered protection
- IPS: matches traffic against known threat signatures to block malware, vulnerability exploits and C2 traffic.
- Cloud-based threat analysis: analyses suspicious traffic in the cloud with AI and ML models to detect unknown threats.
- DNS sinkholing: neutralises DNS requests that would lead users to malicious sites and command servers.
- Sandbox integration: evaluates suspicious files by detonating them safely in WildFire.
- Advanced evasion protection: detects evasion techniques such as domain fronting and steganography.
- Application and IoT security: prevents application abuse and provides dedicated profiles for IoT devices.
Protection against zero-day attacks with deep learning
Thanks to deep-learning models running in the cloud, ATP stops zero-day attacks that exploit vulnerabilities your security team has not yet identified. Suspicious traffic is analysed in real time and unknown threats are blocked immediately.
Neutralise command-and-control (C2) infrastructure
Advanced C2 frameworks such as Empire let attackers remotely control malware they have planted in your network. ATP detects this C2 traffic with deep learning and defeats attackers’ plans to take over your network.
See attacker tactics with MITRE ATT&CK®
ATP classifies and reports the tools and techniques attackers use according to the MITRE ATT&CK® framework, so you can better understand the scope and impact of attacks and be better prepared for the next one.
Benefits of ATP
- Fewer false positives: AI and ML reduce unnecessary interference with legitimate traffic.
- Simple management: central management from a single console (Panorama / Strata Cloud Manager).
- Deep visibility: rich logs to analyse threats and attacks on your network.
- Automatic updates: the cloud-based design keeps protection continuously up to date.
Contact us to add Advanced Threat Prevention to your existing Palo Alto firewall or to position it in a new project; we will manage licensing, profile design and commissioning end to end.
More Palo Alto Networks security services
Frequently asked questions
What is the difference between Advanced Threat Prevention and classic Threat Prevention?
Classic Threat Prevention provides signature-based IPS, anti-malware and anti-spyware protection. Advanced Threat Prevention adds inline deep-learning models running in the cloud that block never-before-seen exploits and command-and-control (C2) traffic in real time.
Does ATP reduce firewall performance?
Because much of the advanced analysis happens in the cloud, no additional resource-hungry analysers are needed on the firewall. A correctly sized appliance delivers the expected throughput with threat prevention enabled; we size it with you during discovery.
Can I add ATP to my existing Palo Alto firewall?
Yes. It is added as a subscription to PA-Series, VM-Series and CN-Series firewalls running a supported PAN-OS version. The Albisec team handles licence activation and security profile configuration.
Talk to our experts about your Palo Alto Networks project
A new deployment, a firewall migration or a support contract: tell us what you need and we will map out the right path with a free initial assessment.